
WooCommerce secure downloads
Secure downloads send customers to a short-lived signed link when they download a purchased file. A shared link stops working after 10 minutes. This works with every storage provider.
How links are signed#
| Provider | Signed link |
|---|---|
| Bunny.net | A link on your downloads pull zone with token and expires (Bunny Token Authentication). Needs a second pull zone, set up below. |
| Amazon S3, Cloudflare R2, DigitalOcean Spaces, Wasabi, Hetzner, Backblaze B2, Google Cloud Storage, other S3-compatible | A presigned URL on your bucket’s storage endpoint, signed with your saved storage keys. No extra setup. |
How it works#
- A customer clicks a download link in their account or order email.
- WooCommerce checks the purchase as usual.
- If the file is offloaded, WP Media Cloud creates a link valid for 10 minutes and sends the customer there. Each click creates a new link.
The product can store either its local file URL or its CDN URL: both are recognised, including older http:// and www addresses and server paths. You do not need to update download URLs for secure downloads to work, and it works with Rewrite URLs off.
Protected product files#
WooCommerce keeps product files uploaded through the product screen in a protected woocommerce_uploads folder that visitors cannot open directly. WP Media Cloud only offloads those files when secure downloads are on and your storage can keep them private:
- S3-type storage: uploaded without public access, whatever the bucket’s default is.
- Bunny.net: offloaded once a Token Authentication key is saved.
- Cloudflare R2 and Backblaze B2: kept on your server, because public access is set for the whole bucket.
If a bucket policy makes every object public, that cannot be overridden from WordPress; check your bucket settings.
If a link cannot be signed, a protected file is never handed out as a plain CDN address: it is served from your server if it is still there, or the download is refused with “This download is temporarily unavailable. Please contact the store.” Regular media that is already public on your CDN still downloads from its CDN address.
File download method#
Under WooCommerce > Settings > Products > Downloadable products > File download method, all three methods are signed: Force downloads, X-Accel-Redirect/X-Sendfile and Redirect only.
Set it up: every provider except Bunny.net#
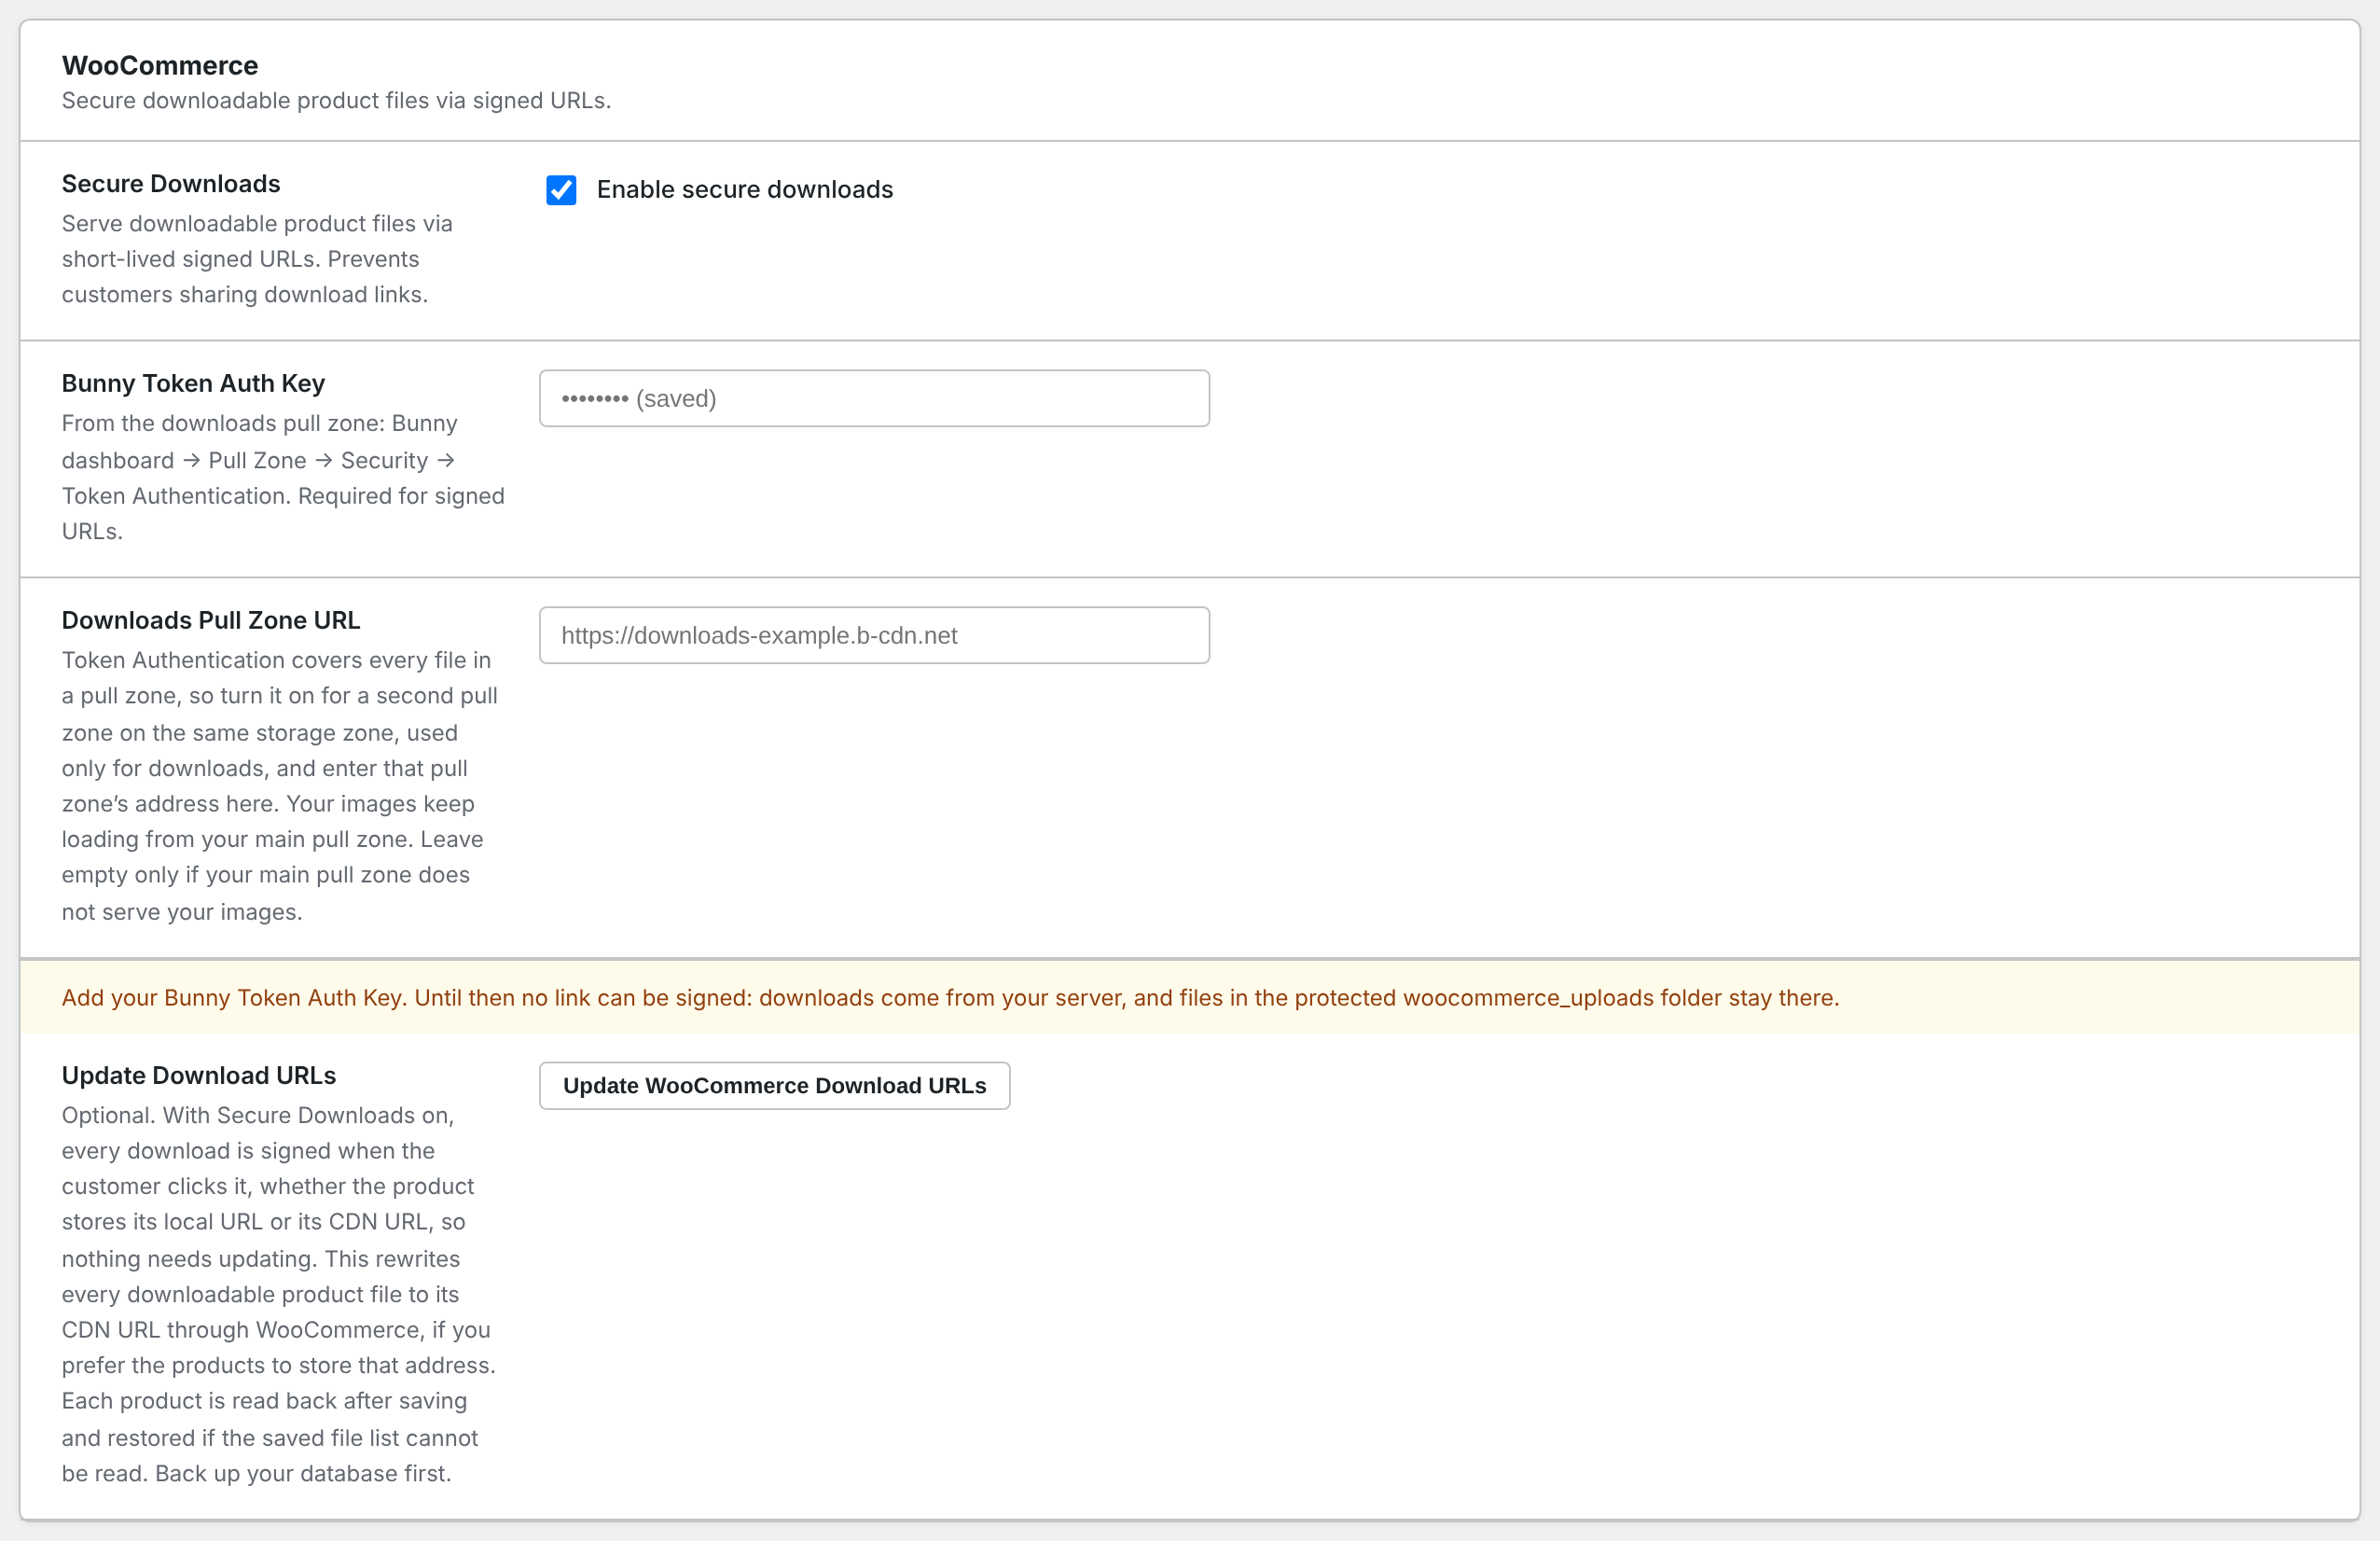
- Go to Media Cloud > Settings and find the WooCommerce card.
- Tick Enable secure downloads.
- Click Save Settings.
- Run a bulk offload, so protected product files that were kept on your server are offloaded.
Set it up: Bunny.net#
Bunny Token Authentication protects every file in a pull zone, so it cannot be turned on for the pull zone that serves your images: they would stop loading. Signed downloads use a second pull zone instead.
- In the Bunny dashboard, go to CDN > Add Pull Zone and choose your storage zone as the origin. Name it for downloads, for example
yoursite-downloads. - In the new pull zone, open Security > Token Authentication, turn it on, and copy the URL Token Authentication Key.
- In WordPress, go to Media Cloud > Settings and find the WooCommerce card.
- Tick Enable secure downloads.
- Paste the key into Bunny Token Auth Key, and the new pull zone’s address (for example
https://yoursite-downloads.b-cdn.net) into Downloads Pull Zone URL. - Click Save Settings, then run a bulk offload.
Your images keep loading from your main pull zone. The key is stored as a secret: the field only shows that a key is saved.
Update Download URLs (optional)#
Update WooCommerce Download URLs rewrites every downloadable product file to its CDN URL, if you prefer products to store that address. You do not need it: with secure downloads on, every download is signed when the customer clicks it, whichever URL the product stores. Back up your database before running it.
It runs in batches with progress and covers simple products, variable products and variations in any status. It reports why any file was left as it is: already on the CDN, not offloaded yet, not in the Media Library, or a link to another site.
Each product’s file list is read back after WooCommerce saves it. If the saved list cannot be read, or does not hold the new URL (for example because another plugin changed the data on save), the original is put back exactly as it was and the product is reported as not saved. Products whose stored file list is already damaged are skipped and reported, never saved over: open each one and save its downloadable files again.
If a product cannot be saved, the button says so and carries on with the rest. The usual cause is WooCommerce’s Approved download directories: add your CDN URL under WooCommerce > Settings > Products > Approved download directories.
Test it#
- Create a test product with an offloaded file.
- Place a test order and click the download link with your browser’s Network tab open.
- Confirm the redirect address contains
tokenandexpires(Bunny.net, on your downloads pull zone) orX-Amz-Signature(other providers). - Wait more than 10 minutes and open the same address. It should be refused.
- Check that normal images on your pages still load.
If the old link still works after 10 minutes on Bunny.net, Token Authentication is not on for the downloads pull zone.